Overview
Our team competed at Pwn2Own Ireland 2026, held in Cork from October 6 to 9. We remotely exploited the Google Pixel 10 and Samsung Galaxy S26 through attacks initiated when a user opened a link. We also achieved code execution against OpenAI Codex and Oracle Autonomous AI Database.
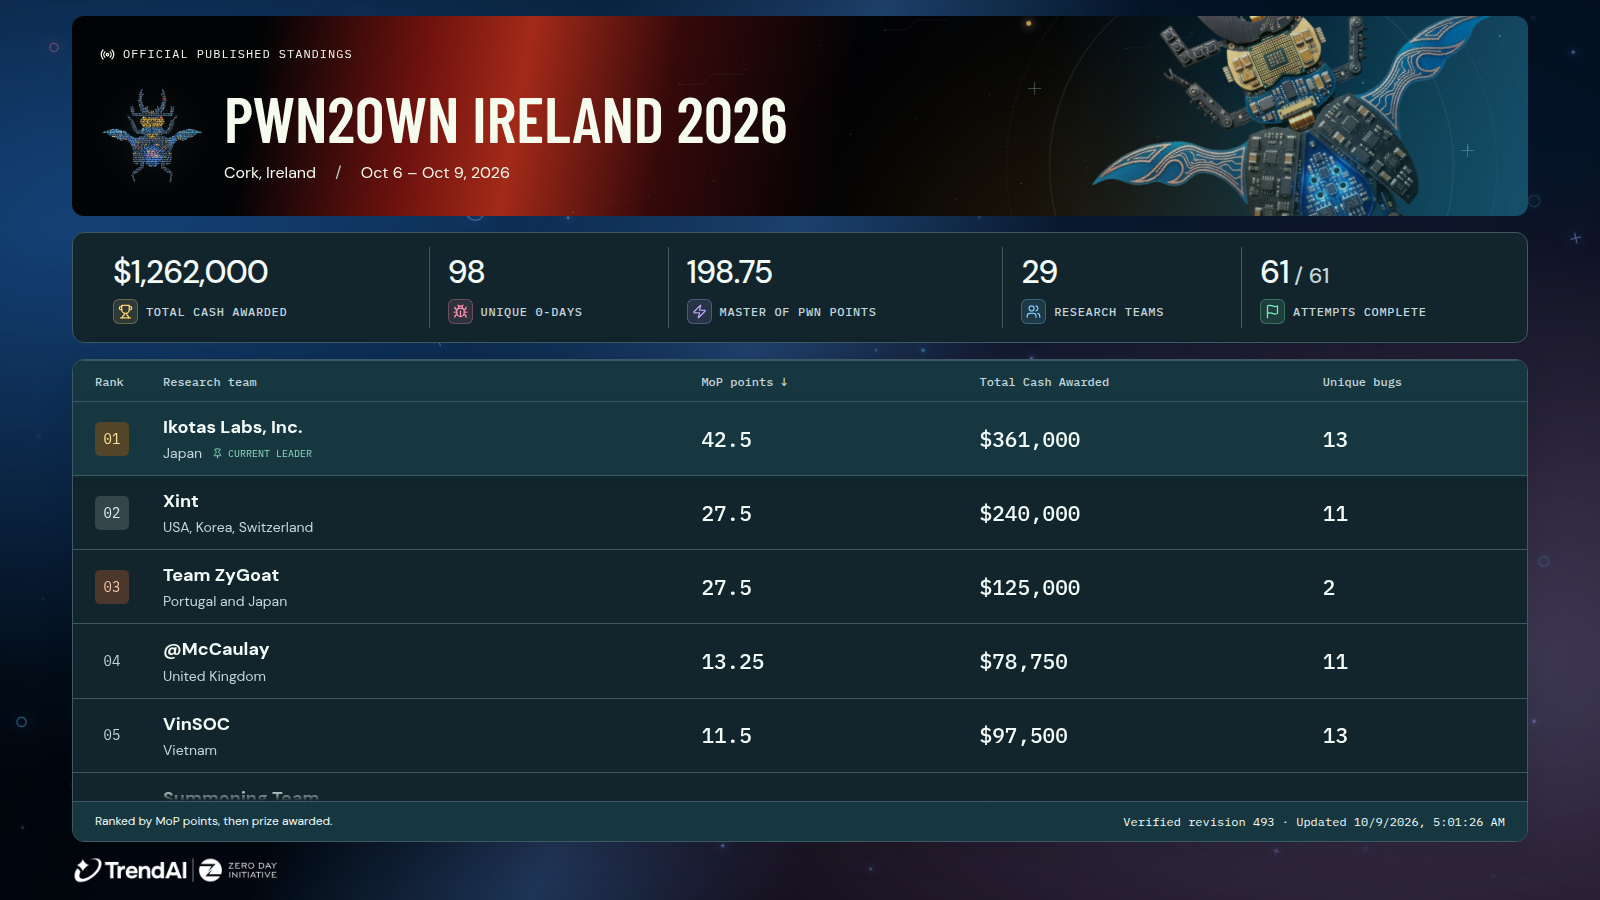
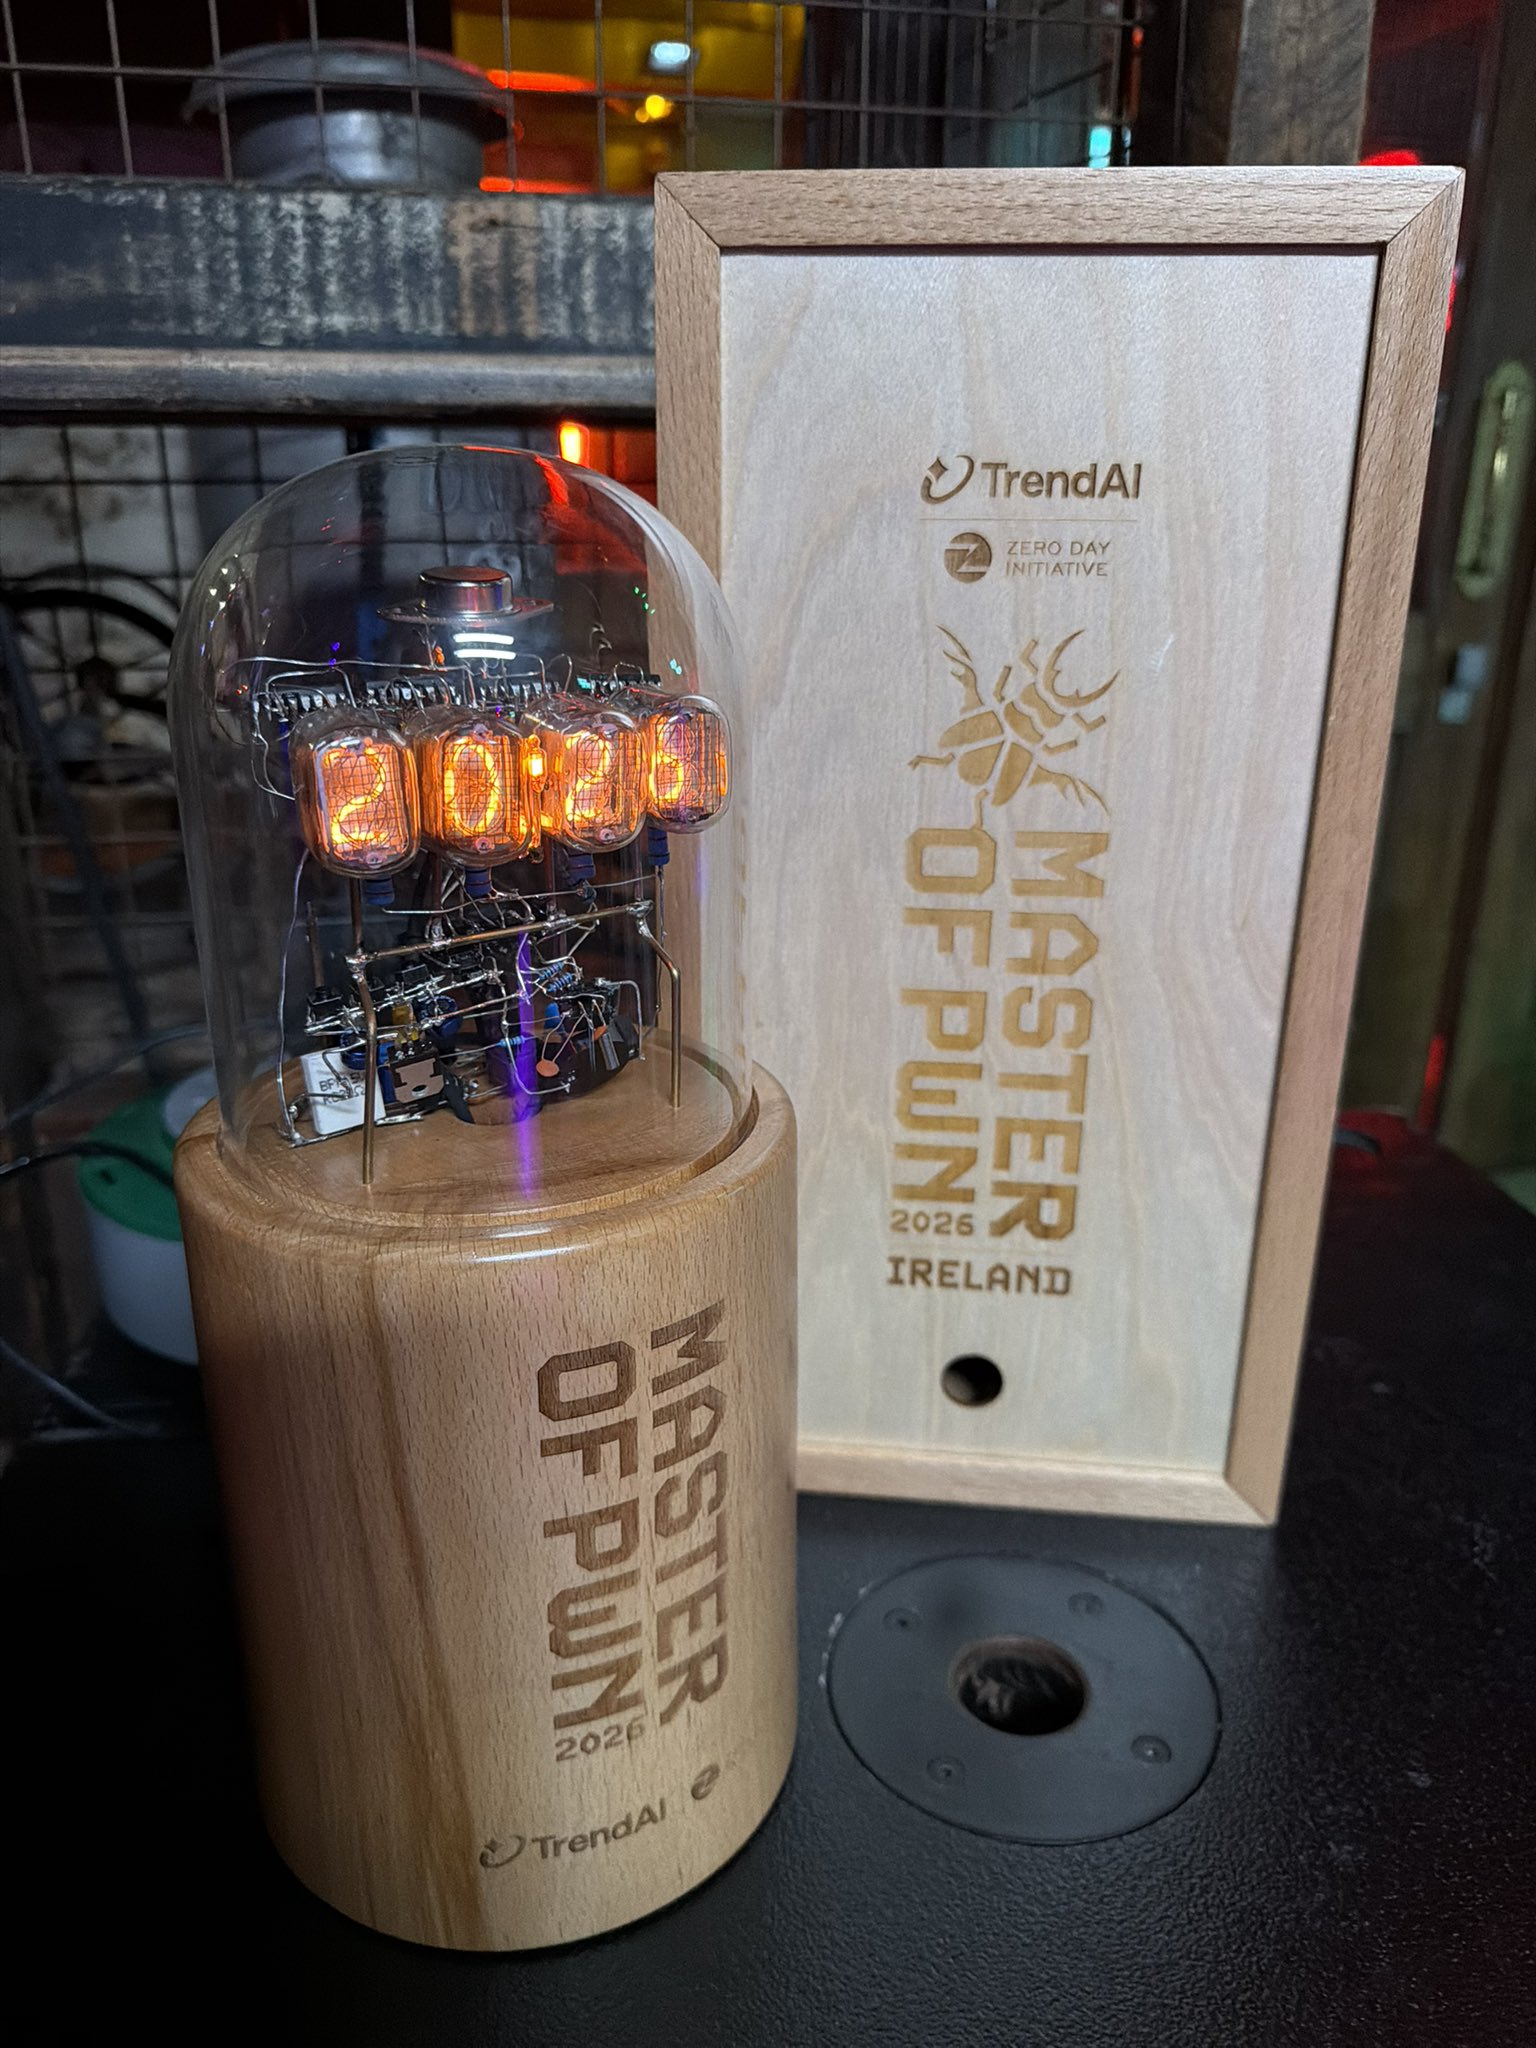
The final tally was 13 unique vulnerabilities, $361,000 in prize money, and 42.5 Master of Pwn points. Ikotas Labs finished first among 29 teams, 15 points ahead of second place, and earned the competition’s overall championship title: Master of Pwn. We are the first Japanese company to win the title.
What Is Pwn2Own?
Pwn2Own is one of the world’s premier hacking competitions, organized by TrendAI’s Zero Day Initiative (ZDI). Researchers use previously undisclosed vulnerabilities to attack current products such as smartphones, AI systems, and smart-home devices on stage.
A vulnerability is a security flaw in software or hardware. An unknown or undisclosed vulnerability for which a fix is not yet available is commonly called a zero-day. Contestants must demonstrate that their exploit works within a strict time limit. After a successful entry, technical details are shared with the organizer and affected vendor so that a coordinated remediation and disclosure process can begin.
Successful entries earn Master of Pwn points based on their difficulty. The team with the highest score across the event becomes Master of Pwn. Competitors must produce working, repeatable exploits against real products to earn these points.
Pwn2Own Ireland 2026 brought together 29 teams for 61 attempts. Across the event, the organizers recognized 98 unique zero-days and awarded $1,262,000.
Five Targets Across Three Days
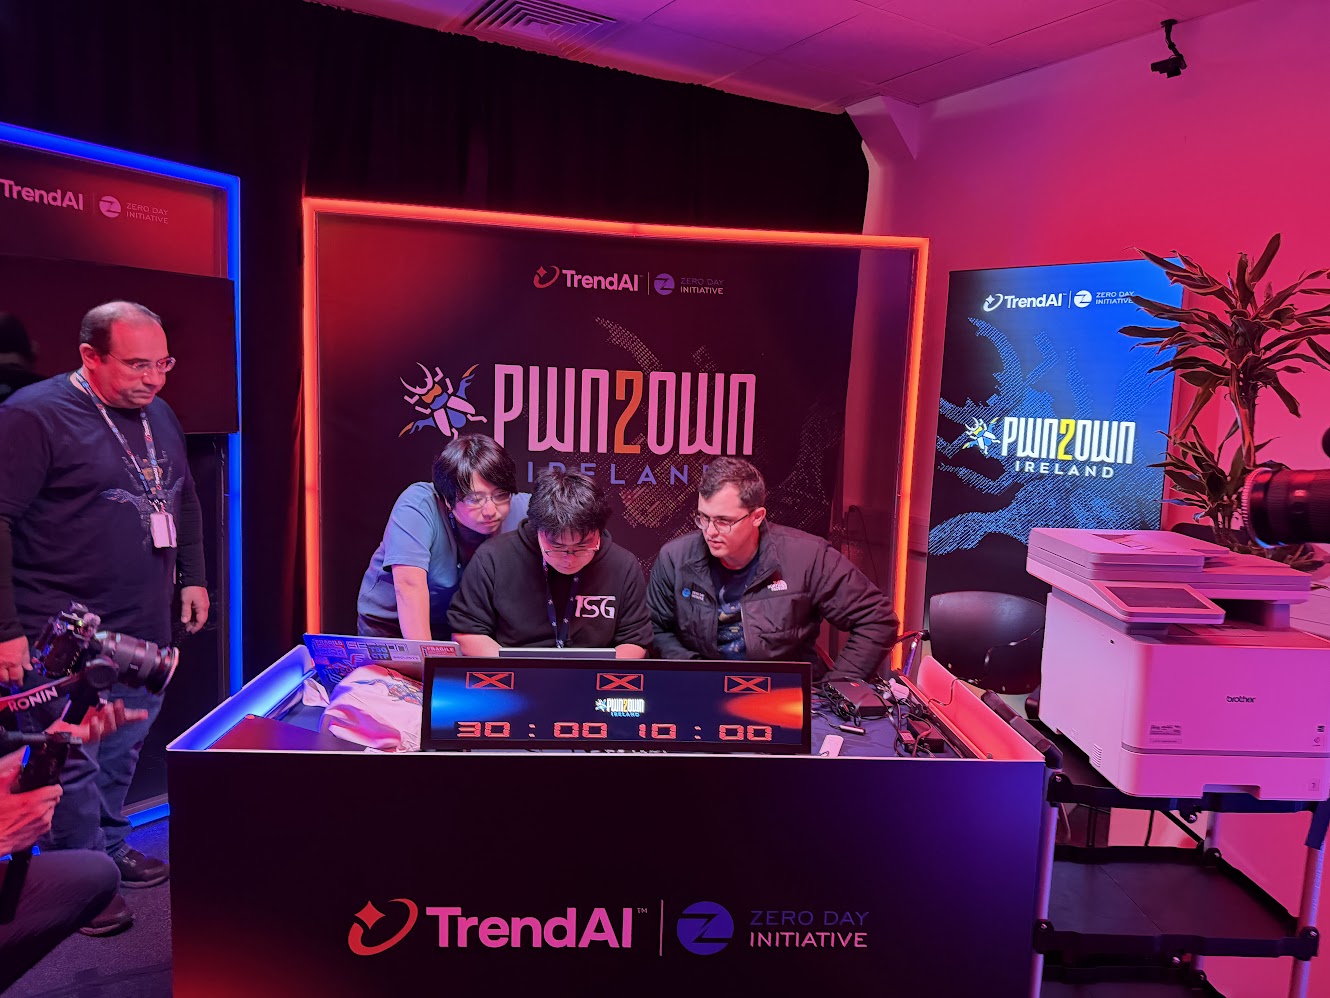
Ikotas Labs entered five attempts spanning four categories: printers, mobile phones, AI coding agents, and AI infrastructure. Our first attempt against the Brother MFC-L8970CDW did not complete within the time limit. We then delivered four consecutive successful exploits.
| Day | Target | Result | Prize | Points |
|---|---|---|---|---|
| Day 1 | Brother MFC-L8970CDW | Unsuccessful | $0 | 0 |
| Day 1 | Samsung Galaxy S26 | Successful | $11,000 | 4.5 |
| Day 1 | OpenAI Codex | Successful | $40,000 | 4.0 |
| Day 2 | Oracle Autonomous AI Database | Successful | $10,000 | 4.0 |
| Day 3 | Google Pixel 10 | Successful | $300,000 | 30.0 |
| Total | Four successes in five attempts | $361,000 | 42.5 |
Day 1: Taking Down a Smartphone and an AI Agent
Remote Control of a Samsung Galaxy S26 from a Link
Our first success came against the Samsung Galaxy S26. We chained four vulnerabilities to demonstrate that opening an attacker-controlled link could cause the phone to run the attacker’s code. This is known as remote code execution (RCE): an attacker can execute operations from elsewhere without physically handling the device.
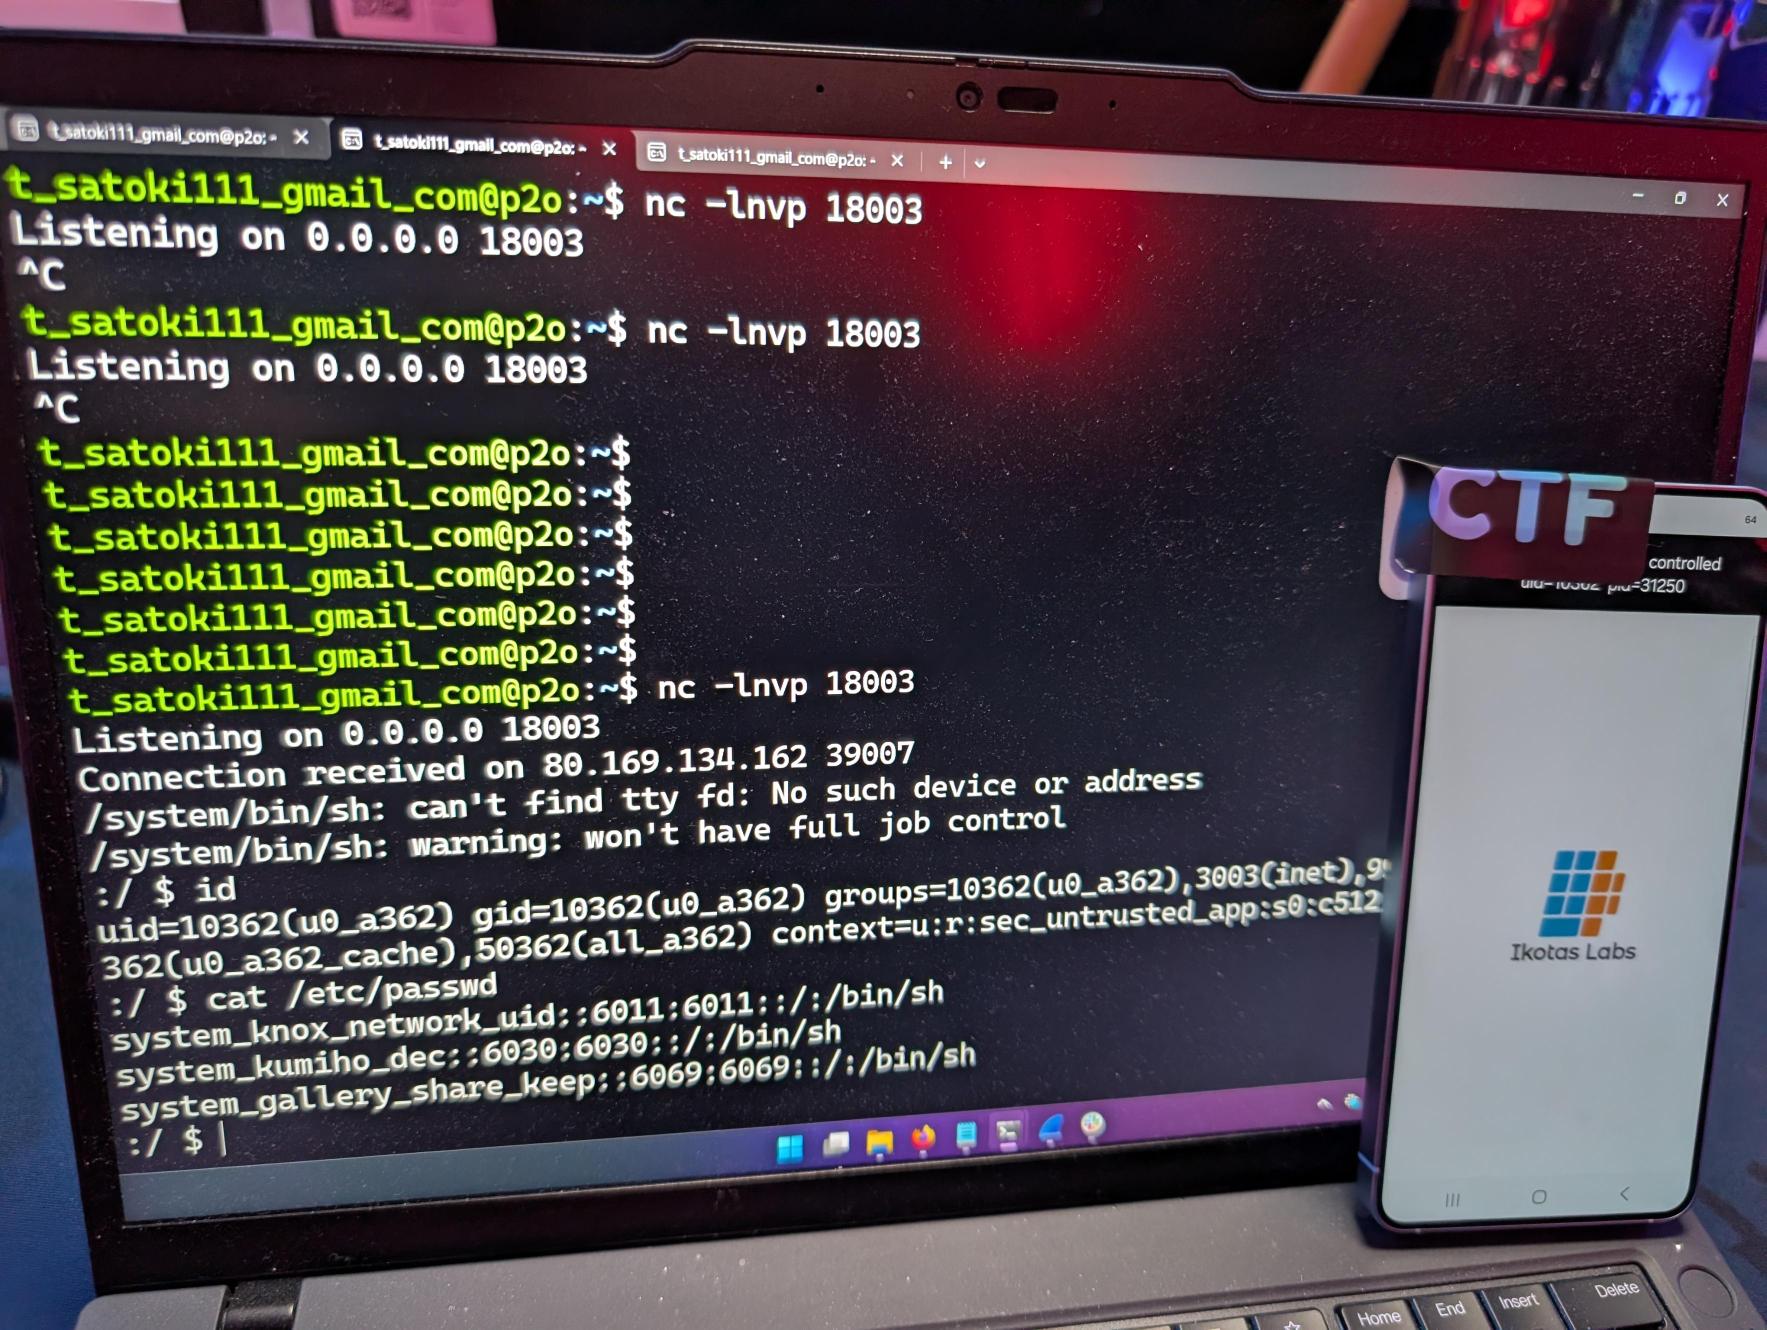
Image courtesy of Zero Day Initiative
One of the four vulnerabilities partially overlapped with an issue that the vendor already knew about but had not yet patched, so that portion was treated as a bug collision. A bug collision occurs when independently prepared research overlaps with a vulnerability already reported to the vendor by the time of judging. The exploit still succeeds, but the overlapping portion receives reduced prize money and points. This entry earned $11,000 and 4.5 points.
OpenAI Codex Exploited at Two Consecutive Pwn2Own Events
Later that day, we successfully exploited the OpenAI Codex AI coding agent. The entry demonstrated an argument-injection vulnerability that allowed attacker-controlled input to trigger an operation that should not have been permitted. It was accepted as a unique zero-day and received the full $40,000 and four points.
We also successfully exploited OpenAI Codex at Pwn2Own Berlin 2026, making this our second consecutive Pwn2Own success against the product. Ikotas Labs was the only team to successfully exploit OpenAI Codex at Pwn2Own Ireland 2026.
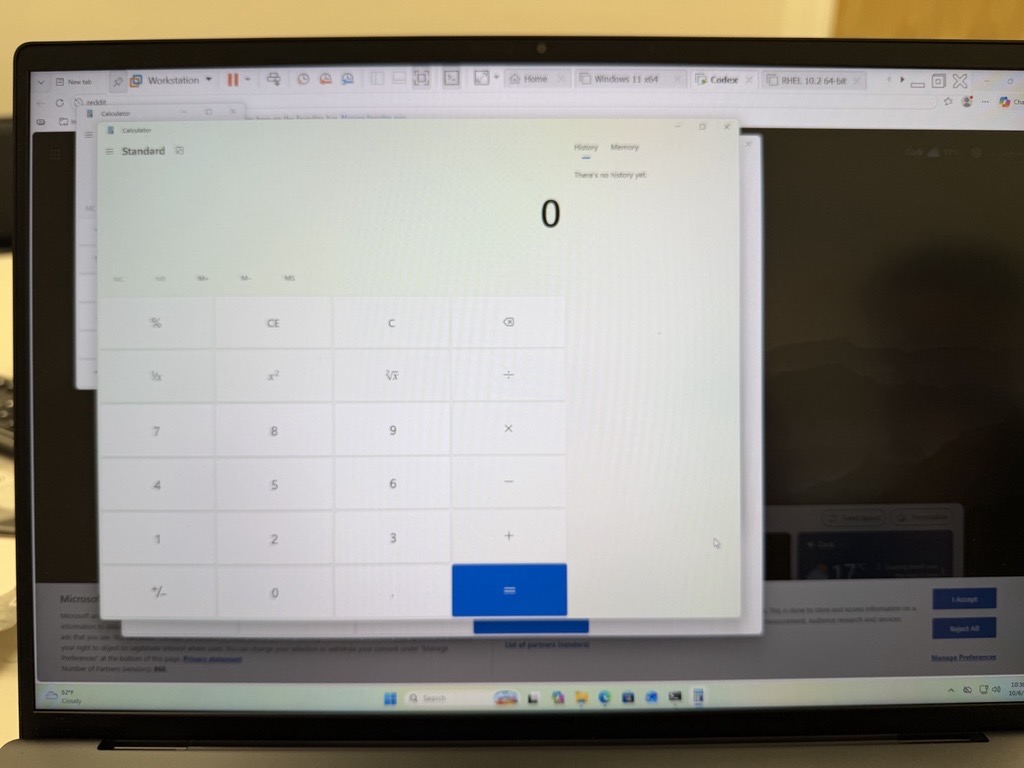
Image courtesy of Zero Day Initiative
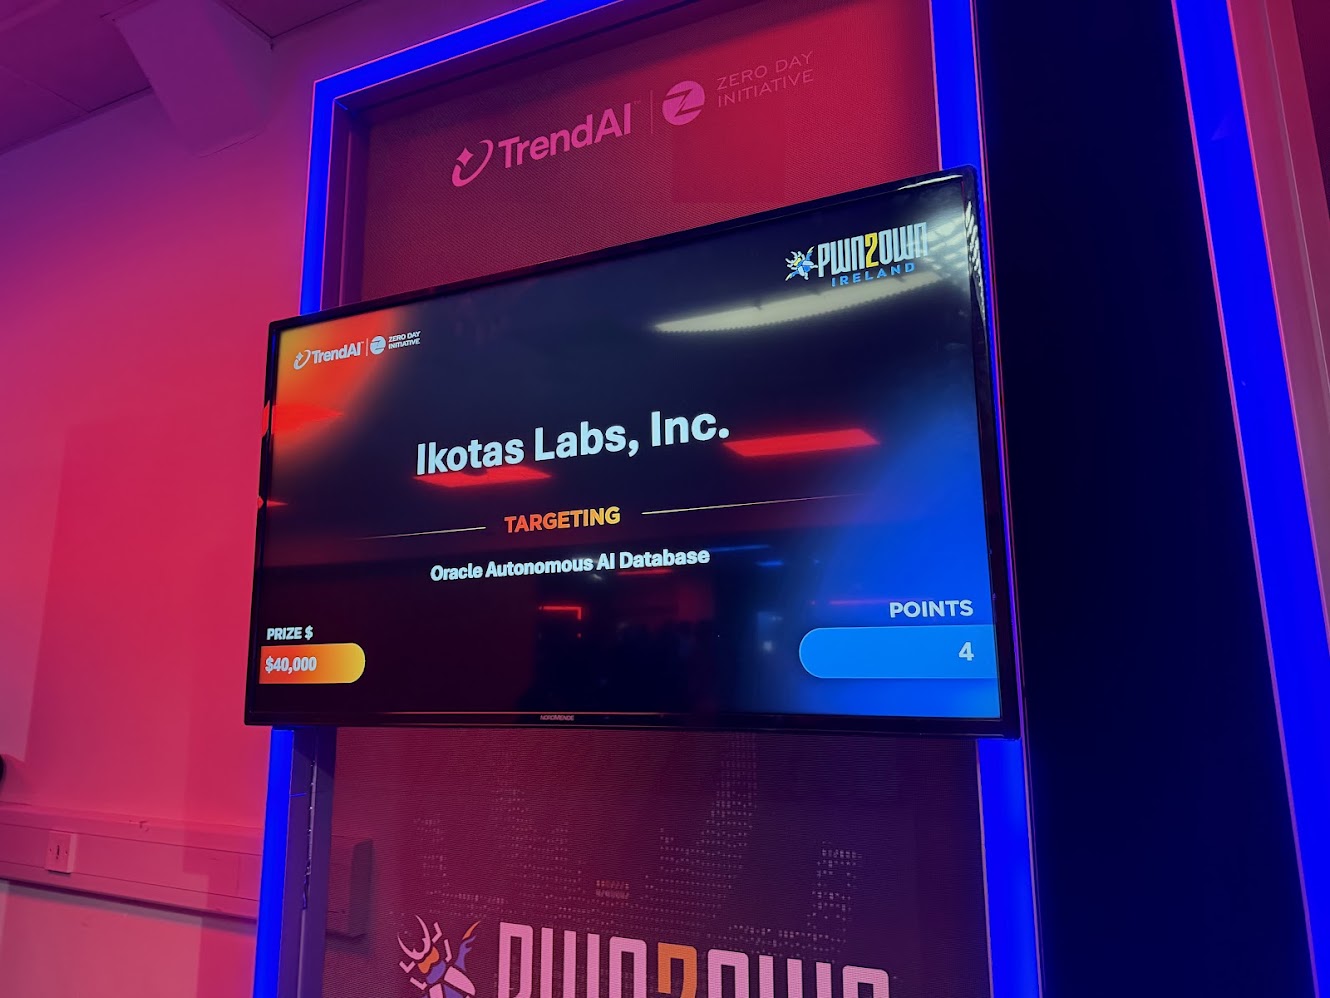
Day 2: Seven Vulnerabilities Chained Against Oracle’s AI Database
On day two, we targeted Oracle Autonomous AI Database. A single vulnerability is not always enough to reach the final objective. Researchers often combine separate flaws into one path that gains an initial foothold, crosses security boundaries, and ultimately reaches code execution. This is called an exploit chain.
We chained seven vulnerabilities, ending with memory-corruption issues known as use-after-free and type confusion, to achieve remote code execution in the database environment. The exploit connected an application-facing entry point to low-level manipulation of program memory.
This result drew on our hybrid research approach, combining AI-assisted vulnerability discovery developed at Ikotas Labs with analysis by human security researchers. All seven issues were accepted as unique vulnerabilities. The entry earned $10,000 and four points; prize amounts can also vary based on attempt order against the same target.
Day 3: Google Pixel 10 Win Sends Ikotas Labs to First Place
On the final day, we attempted the event’s highest-value target: a remote exploit of the Google Pixel 10, worth $300,000 and 30 points. As with the Samsung entry, the attack began when the user opened a link. Our exploit then achieved code execution and demonstrated remote control of the smartphone.
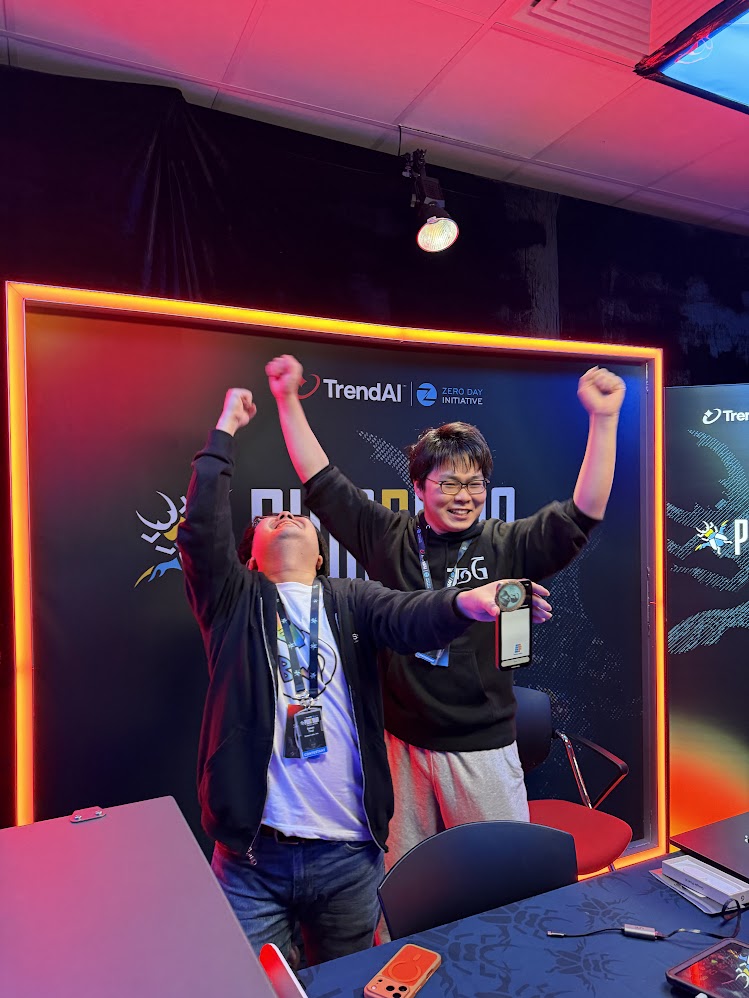
An earlier Google Pixel 10 attempt had succeeded, but its vulnerability was already known to the vendor and the entry received a reduced collision award. Ikotas Labs delivered the event’s first complete Pixel 10 exploit to receive full credit, earning $300,000 and 30 points. The result moved us to the top of the leaderboard, where we remained through the final standings to become Master of Pwn.
Final Results
We successfully exploited several types of targets: smartphones, an AI coding agent, and an AI database. On mobile devices, we demonstrated link-triggered remote attacks against two current Android phones.
The techniques ranged from unsafe input handling and security-boundary violations to application-facing attack surfaces and memory corruption through use-after-free and type confusion. We also combined multiple vulnerabilities into reliable exploit chains and reproduced them on real targets within the competition’s strict time limits.
Our final Pwn2Own Ireland 2026 results were:
- Overall rank: 1st worldwide
- Master of Pwn points: 42.5
- Prize money: $361,000
- Accepted unique vulnerabilities: 13
- Successful attempts: four out of five
Technical Details and Responsible Disclosure
The vulnerabilities used in these entries have been shared with the affected vendors through ZDI and are entering coordinated remediation and disclosure. To protect users, we will not publish vulnerable components, reproduction procedures, proofs of concept, or other attack-enabling technical details until fixes are complete.
Vulnerability Assessments and Penetration Testing
We provide vulnerability assessments, penetration testing, red-team exercises, and product-security evaluations. Our work draws on the experience demonstrated at Pwn2Own across mobile devices, AI agents, AI infrastructure, web attack surfaces, and memory corruption.
We test how far an attacker could progress, identify practical attack paths, and report which risks should be addressed first. To discuss a security evaluation for your product or service, please contact us.