Overview
Ikotas Labs is launching its Attacker-Led Rapid Web Penetration Test for internet-facing services such as Web applications, APIs, and administrative interfaces.
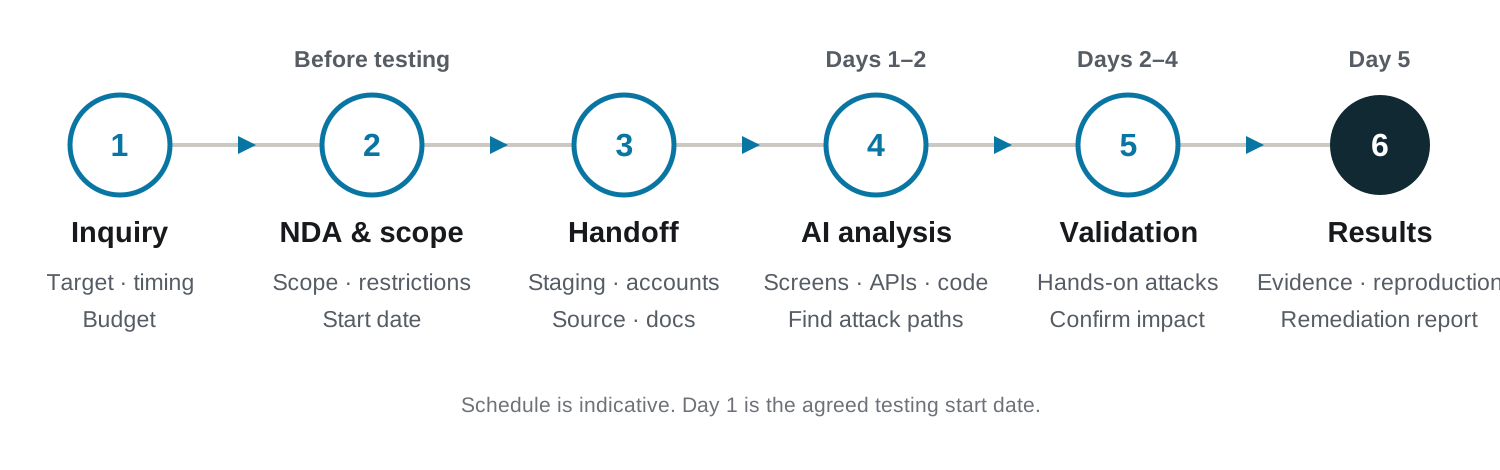
The service combines AI-assisted source-code analysis with hands-on attack validation by human security researchers. We investigate whether an attacker could reach customer data, administrative functions, cloud infrastructure, or other critical assets. The agreed testing start date becomes Day 1, and the assessment report is delivered in principle within five business days.
Here, “Web” does not mean public websites alone. The scope can also include APIs used by mobile applications and business systems, login pages, administrative interfaces, and other internet-facing services.
| Item | Details |
|---|---|
| Targets | Internet-facing services, including Web applications, Web APIs, and administrative interfaces |
| Period | In principle, five business days from the start of testing |
| Method | AI-assisted research and source review, followed by human attack validation |
| Deliverables | Assessment report |
Pricing
Pricing is quoted individually. Based on the budget provided by the customer, we agree on priority attack paths and scope, then perform the assessment on a best-effort basis within the contracted effort. In the contact form, write “Rapid Web Penetration Test” and include the target system, desired timing, and proposed engagement budget.
Attack Expertise from the World’s No. 1 Team at Pwn2Own Ireland 2026
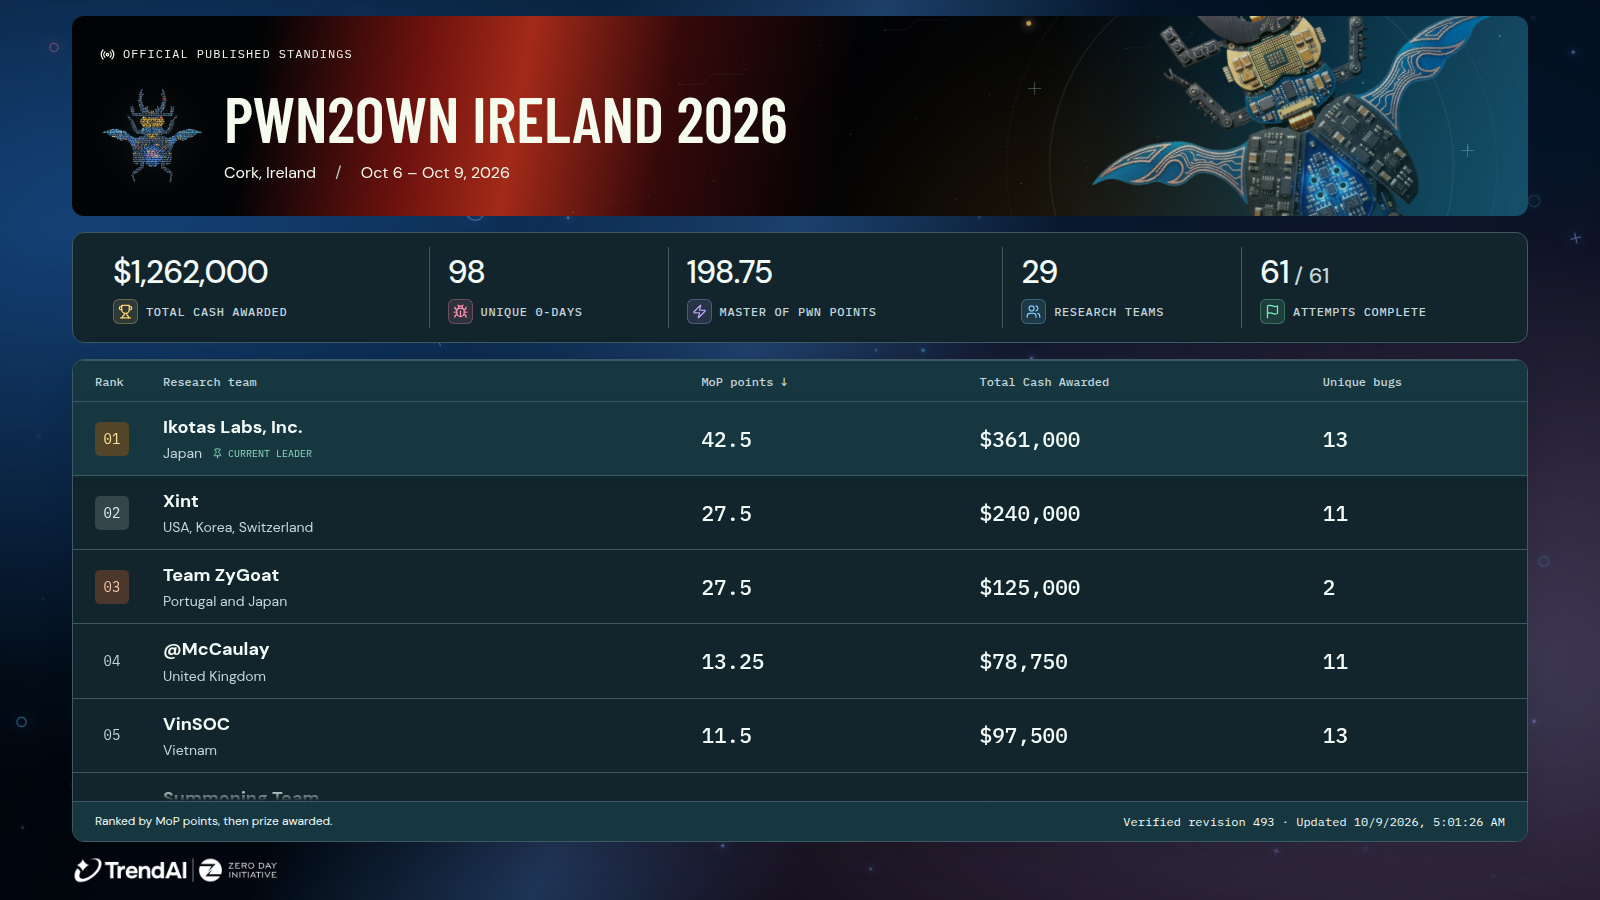
Ikotas Labs placed first among 29 teams at Pwn2Own Ireland 2026 after successfully exploiting Google Pixel 10, Samsung Galaxy S26, OpenAI Codex, and Oracle Autonomous AI Database. We apply the attack expertise that earned the team the “Master of Pwn” title to finding paths from internet-facing services to data exposure before real attackers do. See our full competition results.
Background
In response to unauthorized-access and data-leak incidents, Japan’s Information-technology Promotion Agency issued an urgent advisory on October 9, 2026, asking organizations to review their security controls.
Standard vulnerability assessments can require a long lead time. Automated scanning can identify individual issues, but it does not always establish whether several weaknesses can be chained into a path to customer data or administrative functions.
This service narrows the scope and priorities, using AI for research speed and human expertise for attack decisions, so that practical attack paths can be examined within a short period.
Service Features
Validate what an attacker can ultimately reach
We examine where an attacker could enter, which weaknesses could be chained, and which data or privileges could ultimately become reachable. Findings that appear low-risk in isolation are also evaluated as potential steps in a larger attack path.
AI-assisted research and source-code analysis
AI is used to correlate public information, application screens, APIs, configuration, and source code. This helps identify authorization decisions, data flows, hidden APIs, and dangerous code paths that may be difficult to discover through external testing alone.
AI output is never reported without validation. Human security researchers review each hypothesis and use hands-on testing to establish exploitability and impact.
Report in principle within five business days
The standard scope is one focused internet-facing service. Research, attack validation, and report preparation are performed from Day 1 through Day 5. For large systems or multiple services, we agree on priority functions and attack paths before proposing a schedule.
Primary Test Areas
- Accessing or modifying another user’s information from an ordinary account
- Bypassing authentication or authorization to operate administrative functions
- Controlling a server through file uploads or external URL integrations
- Accessing non-public APIs or administrative endpoints
- Reaching cloud credentials or databases through the Web application
- Reviewing authorization, input handling, and data flows in source code
- Chaining multiple weaknesses to retrieve data at scale
Testing is limited to the internet-facing services and related cloud resources agreed in advance. We do not attack out-of-scope systems or third-party services.
What We Need
After the NDA is signed and scope is confirmed, the customer provides the following two sets of materials. We identify any missing information before testing begins.
- Targets and test environment: Target URLs and APIs, a safe staging environment, role-specific test accounts, protected assets, excluded functions, and prohibited actions
- Source and technical material: A source snapshot or read-only repository, API specifications, architecture diagrams, and external integration details
If source code or a staging environment cannot be provided, we propose a standard vulnerability assessment or penetration test rather than the five-day rapid plan.
Deliverables
Assessment report
The PDF report contains:
- vulnerabilities and severity;
- evidence and reproduction steps;
- root causes;
- recommended remediation.
Additional report items can be included on request.
Light Plan: Web Compromise Indicator Quick Check
This lower-cost plan is intended for organizations that want a focused check for possible compromise before commissioning a full penetration test. We review WAF, Web server, authentication, and cloud logs for suspicious logins, privilege changes, and unusually large data access. Log sources and the review period are narrowed to fit the proposed engagement budget, and the review is performed on a best-effort basis. A fully local LLM can be used when external AI services are not permitted. To request this plan, write “Web Compromise Indicator Quick Check” in the contact form.
Safety and Confidentiality
Testing is performed in staging, with prohibited actions and stop conditions agreed in advance. Source code, credentials, and logs are handled under the NDA; a fully local LLM can be used when external AI services are not permitted.
Contact
After confirming the target scope, desired schedule, and proposed engagement budget, we provide the five-day scope and required materials. In the contact form, write “Rapid Web Penetration Test” and include the target system, desired timing, and proposed engagement budget.
This is a best-effort assessment performed within the testing effort and scope agreed according to the customer’s stated budget. It does not guarantee the absence of vulnerabilities or that no intrusion or data breach will occur after testing.